Last week's question asked if you were creating agents. 65% of respondents are. It's an interesting data point and one I'm glad isn't higher because I believe that our vendors will create all of the agents we might desire. I see the desire to fill a gap by creating an agent a short term problem. A minority perhaps agrees with me and that's OK. There are more unknowns than knowns in AI at this time, which makes everything a speculation.
This also led directly to this weeks survey question.
In the Newsletter this week
I included the Guardz report on the Connectwise backup breach, because the breach is based on an old SkyKick Oauth that many might still have active in their tenant. It's not as simple as deleting it and we don't know how the identity credentials were obtained yet.
Microsoft has a new thing called Project Perception whose job to it watch AI agents and prevent them from acting as an insider threat. It's kinda related to the theme of that breach, because that oAuth permission set was also a trusted app identity. AI agents often have a lot of power and are much more capable. Wrapping insider threat checks around them is going to be a thing.
4 things to know: Working on preventing AI insider threats. Introducing a method for client-driven AI. Microsoft disrupts some of the most annoying phishing scams. Microsoft makes Windows the hybrid agent platform without a running meter.
From Third Tier and B² MSP Advisors:
ThirdTier: Article 4: How to Package and Price IoT Lifecycle Management as an MSP Service
B²: Discount for newsletter readers! $300 0ff. October 27th a small group of MSP start working to make their MSP more valuable
4 things to do: Clean up from the Connectwise backup/Skykick identity breach. Understand Windows new performance features. Create a new habit that prevents risky apps and identities from becoming a Skykick. Security defaults finally get granular
|
|
Have you reviewed OAuth apps access prior to the Skykick/Connectwise breach?
|
I hope that you enjoy this week's newsletter and tell everyone to subscribe.
thanks, Amy
|
|
|
|
|
|
Share this with another M365 admin
|
|
Know someone who would find this useful? Forward this issue and help them stay ahead of Microsoft 365 changes.
|
| |
|
|
|
|
4 things to know: Working on preventing AI insider threats. Introducing a method for client-driven AI. Microsoft disrupts some of the most annoying phishing scams. Microsoft makes Windows the hybrid agent platform without a running meter.
|
|
|
|
|
In the last few months, concerns have arisen about AI safety as a growing number of incidents were publicly disclosed. These incidents exposed how powerful models have become and how they represent a significant threat if not handled well.
|
 blogs.microsoft.com
|
|
• MAI-Code-1.1 Flash: 137B parameter coding model w/ 256K context window, which is now optimized to run on your PC!
• GitHub Copilot now hands off work to local models like MAI-Code-1.1 Flash, helping projects cost a lot less without sacrificing quality.
• With Hybrid Intelligence, Copilot can now take action directly on the PC and keep sensitive work on your device.
• And with Code in Copilot, you can essentially build any software you need on your desktop, without any cloud token spend, and it’s just super at it. You’re no longer limited to what’s in an app store! Your PC becomes an infinite software factory.
|
 blogs.windows.com
|
|
|
|
Microsoft and Health-ISAC are disrupting YAM Store, CoGUI and Iron Man, services that enabled more than one billion malicious messages targeting organizations worldwide.
|
 blogs.microsoft.com
|
|
Discover the lessons we learned about enabling different agent-creation tools for employees with different needs internally at Microsoft using Agent Builder.
|
|  www.microsoft.com
|
|
|
|
|
Sponsored · from MSP Radio
The 68-point checklist, rebuilt for how your clients actually run
|
Karl Palachuk's checklist has started thousands of network audits and client assessments since 2005. Version 5.0 is a full rewrite for today's environment: cloud-first, security-first, and AI everywhere, Microsoft 365 included. Use it for your next onboarding, quarterly review or tune-up.
|
| |
|
|
|
From Third Tier and B² MSP Advisors:
ThirdTier: Update your patching service. Article 5
B²: Special $300 off. Meeting time moved to morning. On October 27th a small group starts making their MSPs more valuable.
|
|
|
|
|
What should happen to each device based on the risk it creates, the business process it supports, and the amount of control we actually have?
|
|  www.thirdtier.net
|
|
Best for MSP owners who want accountability, structure and practical guidance as they actively work to increase the value of their asset.
Investment:
- Facilitator-led monthly Workgroup meetings
- 4 month minimum commitment
|
 b2mspadvisors.com
|
|
|
|
|
4 things to do: Clean up from the Connectwise backup/Skykick identity breach. Understand Windows new performance features. Create a new habit that prevents risky apps and identities from becoming a Skykick. Security defaults finally get granular
|
|
|
|
|
ConnectWise Cloud Backup had a identity breach and it has led to MSP tenants receiving new elevated permissions from the hackers.
|
|  guardz.com
|
|
Every day, your PC helps you get things done, stay connected, capture ideas and make time for what you enjoy. That’s why Windows 11 continues to evolve, starting with a faster, more dependable and refined experience. Thro
|
 blogs.windows.com
|
|
|
|
Listen now | Most tenants have the same problem: hundreds of app registrations and service principals, client secrets that were set to expire in a hundred years, permission grants nobody remembers approving, and test tenants that were never cleaned up.
|
 entra.news
|
|
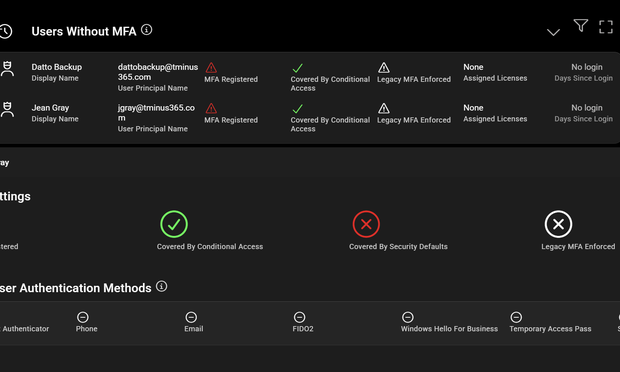
Microsoft is introducing individually managed Security Defaults protections, stronger MFA enforcement, and the ability to use Security Defaults alongside Conditional Access.
|
 tminus365.com
|
|
|
|
|
|